Law / regulation
DPDP Act (India)
India's data protection law for digital personal data, made operational by the DPDP Rules, 2025, which come into force in phases until May 2027.
Cybersecurity · AI Governance · Privacy
MajorCyber™ is an independent knowledge platform that explains security, AI governance and privacy frameworks in clear language, with every claim traced to its official source.
13 full guides 26 profiles Drag the globe to spin it · tap or click a label to open its page · arrow keys move between labels
Focus areas
Governance sets direction. Testing, awareness, intelligence and operations show whether it holds up in practice.
How security programmes are governed, how risk is assessed and treated, and how frameworks turn into evidence.
Building awareness programmes that change behaviour — and meet the training expectations written into major frameworks.
How authorised security testing is scoped, governed and reported, and how findings feed risk decisions.
Running ethical, consent-based phishing simulations that measure risk without punishing people.
Turning threat information into decisions: intelligence requirements, sources, analysis and sharing.
How security operations centres detect, triage and respond — and the reporting duties that follow an incident.
Compliance Academy
Each guide explains what the framework is, who it applies to, what it requires and what evidence looks like.
India's data protection law for digital personal data, made operational by the DPDP Rules, 2025, which come into force in phases until May 2027.
The European Union's binding, risk-based law for AI systems and general-purpose AI models, with obligations that vary by risk level and by role.
The EU's comprehensive data protection law, setting principles, lawful bases, individual rights and accountability duties for anyone processing personal data in its scope.
The international, certifiable standard for building, running and continually improving an information security management system (ISMS).
The first certifiable international standard for an AI management system (AIMS): how an organisation governs the AI systems it develops, provides or uses.
NIST's voluntary, outcome-based framework for understanding, assessing, prioritising and communicating cybersecurity risk, organised into six functions including the new Govern function.
Cyber Intelligence
Short, sourced briefings on regulatory developments, enforcement and incidents, with clear next steps.
All briefingsOne year after India notified the DPDP Rules 2025, Rule 4 on Consent Managers comes into force. Core Data Fiduciary obligations follow eighteen months after publication, in May 2027.
The EDPB set out preliminary, non-binding views on smart glasses: wearers, makers and app providers can all be GDPR controllers, and bystanders need clear warning when recording is possible.
The Dutch data protection authority fined Uber for unlawful solely automated decision-making and weak transparency under GDPR Articles 22 and 13. Uber has appealed.
The EDPB adopted draft guidelines on when authorities should fine rather than use other corrective powers under the GDPR. Public consultation runs until 13 November 2026.
AI Governance & Privacy
The EU AI Act's obligations are phasing in, India's DPDP Rules reach their main compliance date in 2027, and certifiable standards such as ISO/IEC 42001 and ISO/IEC 27701 give organisations a way to organise the work. Our guides separate what is binding from what is voluntary.
Explore AI governance & privacyInsights & Resources
AI governance
ISO/IEC 42001, the NIST AI RMF and the EU AI Act are often mentioned together. One is a certifiable standard, one a voluntary framework, one binding law — and that changes everything.
Practical guide
72 hours, 'without delay', 60 days: how breach notification deadlines, thresholds and recipients differ under GDPR, the DPDP Rules 2025 and HIPAA — and how SOC teams should prepare.
Technical explainer
Authorised penetration testing starts long before the first scan. What to agree on scope, authorisation, rules of engagement, reporting and retesting — and what frameworks like PCI DSS expect.
Comparison
SOC 2 is an attestation report; ISO/IEC 27001 is a management-system certification. How they differ in scope, evidence, audience and effort, and when you need both.
Recently reviewed
Every guide shows when it was last reviewed. These are the most recent.
Behind MajorCyber™
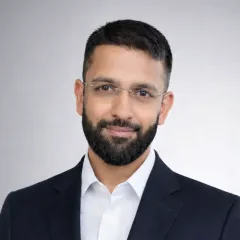
MajorCyber™ was founded by Major Shubham Sharma ("Sam"), a former Indian Army officer and cybersecurity GRC practitioner who holds the CISSP, CCSP and ISACA AAISM certifications and is a BSI-certified ISO/IEC 27001 Lead Implementer. The platform exists to make complex security, AI and privacy requirements understandable, accurately and without hype.